Alice & Bob's ePrint 2026/2665 of 28 October 2026 Puts RSA-2048 at 22,593 Cat Qubits and 3.14 Days, Assuming a Bit-Flip Time of About 100 Years
What Alice & Bob posted to the IACR ePrint Archive on 28 October 2026
On 28 October 2026 the Cryptology ePrint Archive received and approved paper 2026/2665, "Shor's algorithm compiled on cat qubits: 22 593 qubits for RSA-2048 in 3.14 days". Nine of its ten authors work for Alice & Bob, the Paris company that builds superconducting cat qubits; the tenth, André Schrottenloher, is at Inria and the University of Rennes. The paper compiles Shor's algorithm from its mathematics down to the placement and scheduling of physical qubits on a chip, and reuses the result for Bitcoin's secp256k1 curve: at most 30,000 cat qubits and one hour.
Which assumption carries the 22,593-qubit headline
The headline assumes a 1-microsecond error-correction cycle, phase-flip noise of 5 × 10⁻⁴ per cycle and negligible bit flips, which the authors equate to a characteristic bit-flip time of about 100 years. With an extra distance-3 code, a bit-flip time of about one hour suffices and the count rises to about 45,000 cat qubits. In September 2025 Alice & Bob reported an average bit-flip time of 44 minutes, with a 95% confidence interval of 33 to 60 minutes, for one fully characterized cat qubit, plus preliminary traces above three hours on three other qubits that the company says are not by themselves enough to claim the same level of control.
Why the estimate leaves the 2030 dates where they are
The RSA-2048 resource estimate moves the attack cost again, but NIST's final IR 8547 and the HKMA's 2030 aim were set without it. The paper is a company preprint, not yet peer-reviewed, and its value lies in stating every hardware number an attacker would need.
Hong Kong's Banks Scored 2.3 out of 10 on Quantum Readiness in July 2026: What the HKMA and HKUST Post-Quantum Cryptography Toolkit of 2 November Asks Them to Build by 2030
What the Hong Kong Monetary Authority measured in July 2026
On 27 July 2026 the Hong Kong Monetary Authority (HKMA) published a whitepaper on the quantum preparedness of Hong Kong's banking sector and the first Quantum Preparedness Index. The sector scored 2.3 on a ten-point scale built from four dimensions: Awareness, Planning, Pilots and Practical Preparedness. About half of the banks surveyed in early 2026 had no formal post-quantum planning, and about 32% had not started their transition. The HKMA set full sectoral readiness, a score of 10, as its aim for 2030.
What the HKMA and HKUST released on 2 November 2026
Three months later the HKMA and the Hong Kong University of Science and Technology launched a post-quantum cryptography toolkit for banks, announced during Hong Kong FinTech Week and sent to all authorized institutions by circular. It gives a framework for governance and accountability, cryptographic exposure, transition needs and implementation monitoring, plus practical tools for inventories, priorities, supplier engagement and timelines.
Why the Hong Kong timeline matters outside Hong Kong
The HKMA has turned post-quantum migration into a number a supervisor reports and a target year it has chosen itself. That year matches the 2030 deprecation point in NIST's final IR 8547 of 27 October 2026. The index's weights and the number of banks surveyed remain unpublished, which limits comparison with other markets.
NAACP v. xAI in October 2026: Judge Brown Refuses the Justice Department's Dismissal on 19 October and xAI's Motion to Dismiss on 30 October in the Clean Air Act Suit Over the Southaven Gas Turbines
What the Northern District of Mississippi decided on 19 and 30 October 2026
In NAACP v. X.AI Corp., No. 3:26-cv-74, U.S. District Judge Debra M. Brown granted the United States' request to intervene on behalf of the EPA Administrator on 19 October and denied its request to dismiss the case. On 30 October, according to the plaintiffs' counsel, the court also denied xAI's own motion to dismiss. The NAACP and its Mississippi State Conference sued xAI and its energy affiliate MZX Tech on 14 April 2026, alleging that the gas-fired turbines of the Colossus Gas Plant in Southaven were built and run without a Clean Air Act permit. The plant sits about a mile across the state line from xAI's Colossus 2 data center in South Memphis.
Why the ruling matters for AI infrastructure
The government argued that, once inside the case, it could end it unilaterally, and it cited national security and the importance of AI. The court found no such power in the statute's citizen-suit provision, 42 U.S.C. § 7604, and did not treat the national-security concerns as relevant to that question. The second ruling, as counsel describes it, rejected xAI's arguments that citizen suits are unconstitutional and that the turbines are exempt mobile sources. The preliminary-injunction request is still undecided. This post reconstructs how the case reached this point and what it shows about AI data center power as a question of environmental law, enforced by the people who live beside the turbines as well as by federal agencies.
Can an NHS Trust Blame the Developer When Diagnostic AI Fails? What the UK Jurisdiction Taskforce's July 2026 Liability Statement and the MHRA Commission's Recommendations Say
What the UK Jurisdiction Taskforce concluded in July 2026
The UK Jurisdiction Taskforce, chaired by the Master of the Rolls, published its 130-page Legal Statement on Liability for AI Harms in July 2026 after a public consultation on a draft. Its central finding is that the existing private law of England and Wales can resolve claims for harm caused by AI without a new liability regime. AI has no legal personality, so liability attaches to the developers, providers and users behind it. Contract allocates risk along an AI supply chain first, and negligence fills the gaps.
Why hospitals and clinicians read it closely
The statement treats an NHS Trust's duty to its patients as non-delegable: a Trust cannot escape liability for a defective diagnostic tool by pointing at the developer. It also says a clinician may be liable for failing to use AI where a competent practitioner would have used it; its own example is a radiologist who ignores an effective tumour-detection tool available at reasonable cost. Browne Jacobson's 30 October 2026 reading sets the statement beside the MHRA National Commission's recommendations of 10 September 2026. This post asks who answers when a diagnostic AI fails, and where the EU's new Product Liability Directive draws the line differently by treating software as a product.
Could Executives Who Supply AI Targeting Systems Face Rome Statute Liability? The ICRC Blog's 29 October 2026 Case for Article 25(3)(d)(ii) and the Katanga Test
What the ICRC Humanitarian Law & Policy blog published on 29 October 2026
Rosa Villar Orero, a PhD candidate at the University of Aberdeen, argues in the ICRC's Emerging Voices series that senior executives of companies supplying AI targeting systems could, in principle, be criminally responsible under the Rome Statute when their systems contribute to war crimes. Her route runs through Article 25(3)(d)(ii), a residual form of accessory liability for anyone who intentionally contributes to a crime committed by a group acting with a common purpose, with knowledge of the group's intention. The piece is a scholarly argument published on an ICRC platform and should not be read as an ICRC position.
Why the knowledge standard matters for AI vendors
Aiding and abetting under Article 25(3)(c) requires that the supplier act for the purpose of facilitating the crime, which a commercial seller can usually deny. Article 25(3)(d)(ii) asks only for knowledge, and the author applies the five-element test that ICC Trial Chamber II set out in the 2014 Katanga judgment. On her reading, NGO reports, journalism and ICC proceedings can support an inference about what an executive knew of a client's intentions, and that inference, proved against a specific individual, is what could make AI targeting system providers accessories. Public reporting alone does not establish an individual's knowledge, and reported civilian harm does not by itself establish a war crime. The argument extends Rome Statute accomplice liability to software and has not been tested in any court. This post reads the argument element by element and marks where it is strongest and where it is thinnest.
Mauritz Kop and Paul Davies at Co-Opting AI: Quantum: Harvest Now, Decrypt Later, the Quantum Event Horizon, and Surgical Guardrails (Video)
The University of Virginia has published the recording of Co-Opting AI: Quantum, the public conversation of October 28, 2026, in which our founder Prof. Mauritz Kop and the physicist Paul Davies discussed quantum technology and AI with host Mona Sloane. Kop opened with access: "Decisions about access to quantum technologies will shape who can benefit from them and who controls their use." Leadership in quantum technology, he said, could give states enduring power over the world's digital operating system, and he described that lasting shift in strategic power as a quantum event horizon.
The Quantum Apocalypse, Harvest Now, Decrypt Later, and Quantum First
Davies warned that encrypted data already collected by an adversary could be read once a large quantum computer exists: "We may be on the verge of a quantum apocalypse." Kop said that preparing systems with post-quantum cryptography can deny an adversary the benefit of a quantum attack, a form of deterrence by denial, and gave the audience a method for reading the headlines: separate a demonstrated result, a resource estimate, and a commercial forecast.
Surgical Guardrails and a Quantum Workforce
On governance, Kop asked policymakers to learn from the AI, biotechnology, and nuclear governance cycles and to keep interventions surgical, so that innovation can breathe while the United States works to be quantum first. He invited the audience to become the quantum workforce for a values-based American quantum ecosystem.
Delaware's Draft AI Company Act Lets an AI Agent Manage a Firm and Shields Its Sole Member: What the 36-Page Text Says, and What Comer's 26 October 2026 Letter Demands
What Delaware's draft Artificial Intelligence Company Act would create
A 36-page draft House bill, prepared for Delaware's 153rd General Assembly and marked as a draft of 2 June 2026, would add two chapters to Title 6 of the Delaware Code: an Artificial Intelligence Regulatory Sandbox Program and an Artificial Intelligence Company Act. The new entity, the AIC, has exactly one member, and its manager is an AI agent that runs the business and must document every action in a signed record. The program would run for 30 months, banking is excluded, and admission is decided by a committee that includes the Secretary of State, the Attorney General and the Chief Justice. The draft's central feature is a member liability shield that holds while the company stays adequately capitalized.
Why House Oversight wrote to Governor Meyer on 26 October 2026
Chairman James Comer of the House Committee on Oversight and Government Reform asked Governor Matt Meyer for all drafts, outside contributors' agreements, safety discussions and communications on the proposal since 1 January 2025, due by 9 November 2026. The letter says the AIC could protect AI companies and investors "from responsibility for reckless harmful actions" and questions the role of an AI company contributing to the project, which the Secretary of State's own op-ed in Fortune identifies as Norm Ai. It also signals possible federal legislation to limit state AI initiatives, which puts Delaware corporate law and federal preemption on the same table before the bill has even been introduced.
NIST's Final IR 8547 of 27 October 2026 Deprecates P-256, RSA-3072 and Ed25519 After 2030, Where the 2024 Draft Left 128-Bit Keys Untouched Until 2035
What NIST changed in the final IR 8547 on 27 October 2026
NIST published the final version of NIST IR 8547, Transition to Post-Quantum Cryptography Standards, on 27 October 2026, replacing the initial public draft of 12 November 2024. The central change sits in the transition tables. The draft deprecated only quantum-vulnerable algorithms at 112 bits of security after 2030 and let stronger keys run until they were disallowed after 2035. The final deprecates every quantum-vulnerable public-key algorithm at 112 bits or more after 2030, so ECDSA on P-256, RSA-3072 and Ed25519 now enter the deprecated category at the same point as RSA-2048. Disallowance after 2035 stays where it was.
How the final ties NIST standards to EO 14412 and OMB M-26-15
The report now cites Executive Order 14412 of 22 June 2026 and OMB Memorandum M-26-15 of 24 June 2026. Under them, federal high value assets and high impact systems must use post-quantum key establishment by 31 December 2030 and post-quantum signatures by 31 December 2031, and agencies must support TLS 1.3 by 2 January 2030. NIST says the 2030 to 2035 window exists for lower-risk and legacy systems and does not relax those deadlines. The final also names ML-KEM-768 as the default parameter set, confirms HQC as the second key-establishment scheme and states that an approved composite, or hybrid, key-establishment technique can be FIPS 140 validated when at least one of its inputs comes from an approved scheme.
Why the US Energy Department Added Helium to Its Critical Material List on 27 October 2026, and Where Quantum Computing Appears in 91 FR 67558
What the Department of Energy published on 27 October 2026
The US Department of Energy added helium to its Critical Material List in a notice published in the Federal Register on 27 October 2026 as 91 FR 67558. Assistant Secretary Audrey Robertson of the Office of Critical Minerals and Energy Innovation signed it on 21 October. The legal basis is section 7002(a)(2) of the Energy Act of 2020, which lets the Secretary of Energy name materials with a high supply-chain risk that serve an essential function in energy technologies. The notice has no comment period. Helium joins the 18 critical materials for energy on the 2023 list and metallurgical coal, added in May 2025.
Where quantum computing appears in the helium notice
The summary calls helium non-substitutable for semiconductor manufacturing, leak testing of natural gas infrastructure and quantum computing, and essential to medical and scientific uses. The justification in the body rests on chips and AI infrastructure. Quantum computing is named once and is not developed further.
Why the notice matters for dilution refrigerators and helium-3
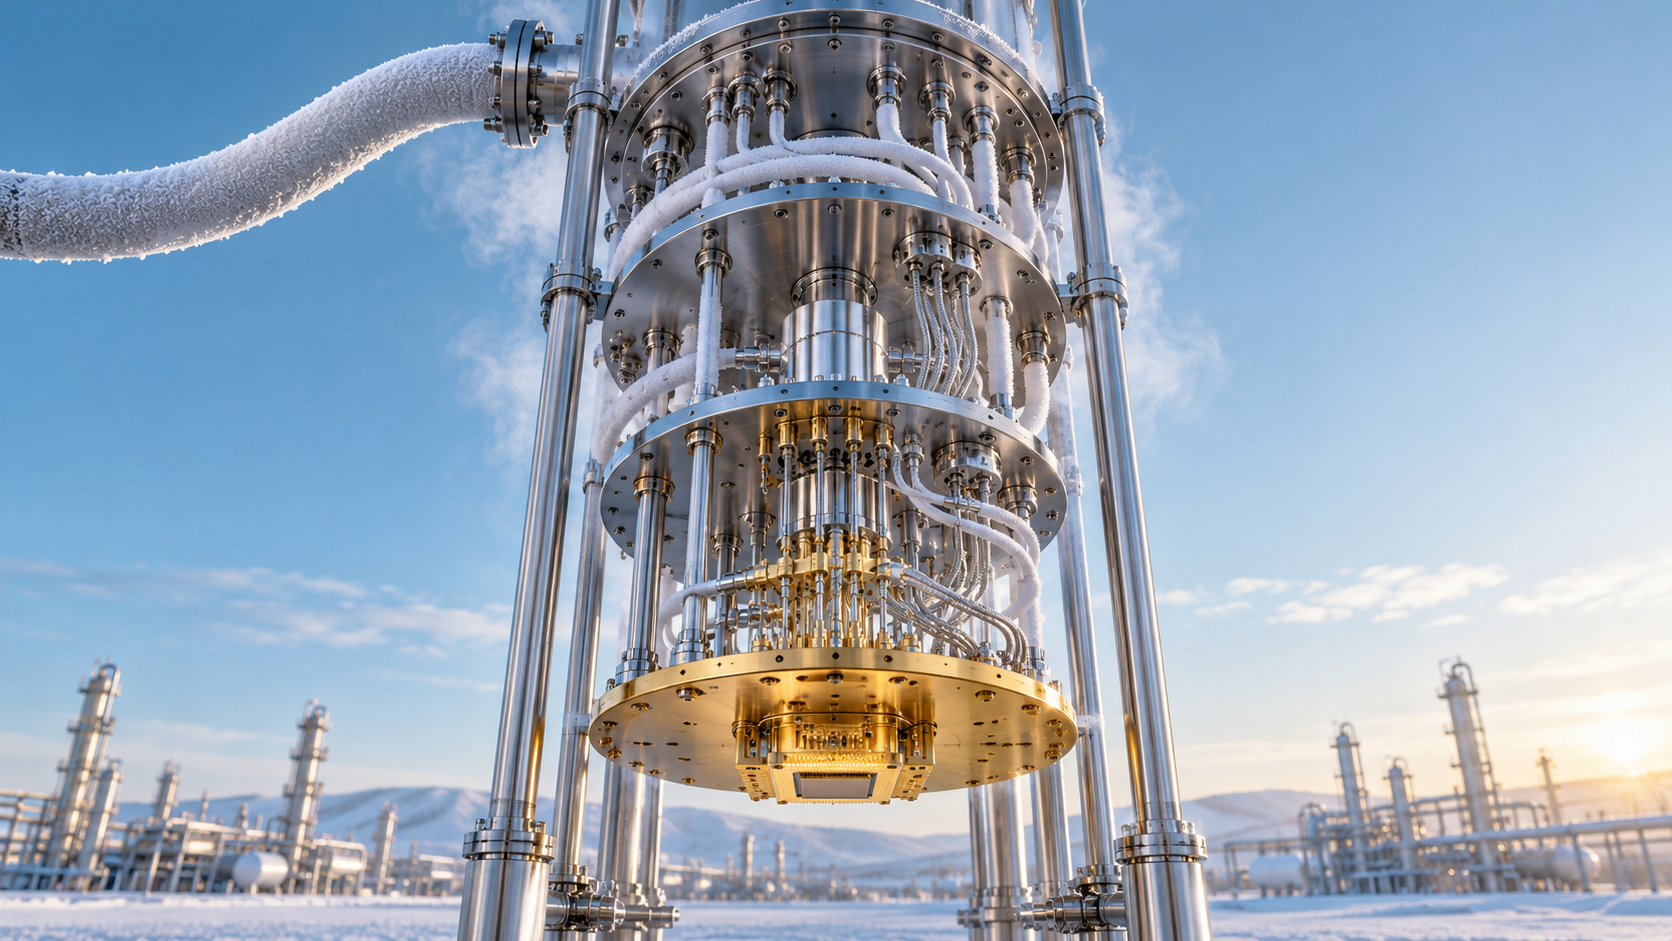
Superconducting and most spin-qubit processors run inside dilution refrigerators that circulate a mixture of helium-3 and helium-4. The designation covers helium without qualification, yet the notice contains no isotope-specific analysis, and helium-3 supply follows its own route: DOE's helium-3 is a byproduct of tritium processing at the Savannah River Site, sold through the DOE Isotope Program. What the designation does for the cold end of the quantum stack depends on what DOE publishes next.
Who Would Check a Florida Child's Age Under the Safe Screens Act? App Stores, Operating Systems and AI Chatbots in the 22 October 2026 Proposal
What Florida's Attorney General proposed on 22 October 2026
Florida Attorney General James Uthmeier released a legislative proposal called the Safe Screens Act on 22 October 2026. It covers three kinds of company at once. App stores would have to determine each user's age, link a minor to a parent's account and obtain parental consent before a minor downloads or buys an app. AI chatbot operators would have to determine the age of every account holder. Operating systems would have to apply age-appropriate restrictions at the device level. The release requires all of this to use "commercially reasonable, privacy-protective methods" and names no method.
What the proposal would bar AI chatbots from offering minors
For every user under 18, chatbot operators could not offer features that simulate companionship through personification, emotional engagement or user-data retention, could not suggest the chatbot is a real person, and could not encourage self-harm, sexual content or isolation from trusted adults. Social media accounts for ages 14 to 17 would get a school-hours and overnight quiet mode, a two-hour daily cap and hidden like counts. Violations would be enforced as unfair practices under section 501.1736 of the Florida Statutes, the 2024 law that already bars social media accounts for children under 14, at up to $50,000 per violation.
Why the operating-system clause decides which company establishes a user's age
No bill text or sponsor has been published. The proposal would still need a legislator to file it before Florida's 2027 regular session, which opens on 2 March 2027. For AI chatbot age verification the design question is already concrete: which layer of a phone learns a child's age first, and which companies may rely on that signal.

What the UK-Singapore Financial Dialogue Joint Statement of 20 October 2026 Says About Post-Quantum Cryptography, QKD and Bank Supervisors
What HM Treasury and MAS published after the 20 October 2026 dialogue
On 20 October 2026 the United Kingdom and Singapore held their 11th Financial Dialogue in Singapore, with officials from HM Treasury and the Monetary Authority of Singapore joined by the Bank of England and the Financial Conduct Authority. The joint statement HM Treasury published the same day runs to roughly a thousand words across digital finance, capital markets, sustainable finance and the two countries' 2027 roles at the G20 and in ASEAN. Quantum technology takes one sentence. It says the exchange covered each side's approach to quantum security and to supervisory expectations for financial institutions moving to quantum-safe technology, including the NCSC's post-quantum cryptography migration guidance and lessons from MAS's quantum key distribution sandbox.
Why the two references in that sentence point in different directions
Some trade coverage described the meeting as an agreement on joint oversight and unified standards. The statement contains no such commitment. Its interest lies in the pairing. The NCSC sets 2028, 2031 and 2035 as its migration milestones and says it will not support quantum key distribution for government or military use. MAS has tested QKD with four banks and reported both its potential and its limits. This post reads the sentence closely and asks what a bank supervised in both London and Singapore can take from it.

The SEC's Fiscal Year 2027 Examination Priorities List Quantum Computing Under Regulation SCI: What the 23 October 2026 Sentence Means for Exchanges and Clearing Agencies
What the SEC published on 23 October 2026
On 23 October 2026 the US Securities and Exchange Commission released the Division of Examinations' priorities for fiscal year 2027. In the section on Regulation Systems Compliance and Integrity, the rule that governs the core technology of exchanges, clearing agencies, FINRA and a few other market utilities, the Division says its examinations "will focus on emerging trends, including SI, tokenization of securities, extended trading hours, and quantum computing." Neither the fiscal 2025 nor the fiscal 2026 priorities mentioned quantum computing at all.
What the Regulation SCI sentence requires of exchanges and clearing agencies
Several outlets reported that the SEC is now targeting quantum computing. The document is narrower. It names no algorithm, sets no migration date and asks for no inventory, and its own disclaimer says it is a staff statement with no legal force. The weight comes from the rule it sits under. Regulation SCI already requires each covered entity to keep written policies that give its systems adequate security, and to review and test those systems for vulnerabilities to internal and external threats. An examiner who asks how a clearing agency is preparing for post-quantum cryptography can now point to a published priority when asking. This post compares what was reported with what the text says, and asks what an SCI entity can expect to be asked in the coming fiscal year.
Prof. Mauritz Kop Chairs CIGI's Quantum Nexus Panel and Roundtable: What Sarrao, Karanicolas, Dekker, Murphy, and Minssen Said (Video)
CIGI has published the recording of The Quantum Nexus, the public expert panel that our founder Prof. Mauritz Kop chaired on October 21, 2026, as CIGI Senior Fellow and Principal Investigator of a project supported by Canada's Department of National Defence. Kop opened with one question: how do democracies keep their secrets safe and their science open? He set out the Nexus, which treats patents, trade secrets, export controls, supply chains, and standards as one governance control plane, and his LSI test for measures that are least trade-restrictive, security-sufficient, and innovation-preserving.
Five Experts on Supply Chains, Migration, IP, Standards, and Europe
SLAC Director John Sarrao urged allies to lean open while staying prudent. Michael Karanicolas of Dalhousie examined Canada's post-quantum cryptography roadmap and the privacy stakes of the transition. Patent lawyer Tina Dekker explained why owning IP does not by itself permit a company to export it. Michael P. A. Murphy of Queen's University showed why NATO standards need implementation, and Timo Minssen of the University of Copenhagen proposed interoperability and IP conditions for publicly funded quantum testbeds. CIGI's Tracey Forrest set out the institute's quantum program.
A Closed-Door Roundtable and Six Emerging Scholars
A roundtable under the CIGI Rule followed, with officials from Ottawa, experts from Washington and Los Alamos, and six Emerging Scholars mentored by Kop. Our article summarizes every speaker and what the discussion means for companies that build, buy, or invest in quantum technology.

Treasury's 22 October 2026 COINS Act Proposal Adds Quantum Algorithms and Applications to the Outbound Investment Prohibition: What Section 851.226(j) Says Before 7 December
What Treasury proposed on 22 October 2026
On 22 October 2026 the US Treasury issued a notice of proposed rulemaking to implement the Comprehensive Outbound Investment National Security Act, the COINS Act, which Congress passed in the Fiscal Year 2026 National Defense Authorization Act. The proposal rebuilds the Outbound Investment Security Program that has applied since 2 January 2025 under 31 C.F.R. Part 850. It covers six technology sectors, adds Cuba, Iran, North Korea, Russia and Maduro-era Venezuela to China as countries of concern, and keeps comments open until 7 December 2026.
Why the quantum line moves to software
The existing rule already prohibits US investment in covered companies that build quantum computers and their critical components, and in quantum sensing and networking limited by military, intelligence, mass-surveillance or other specified end uses. The proposal would add the development of quantum algorithms and applications; its preamble promises an end-use limitation for that clause, which the draft rule text does not visibly carry. In AI the notification tier disappears: any covered investment in a company developing what the proposal now calls a super intelligence system would be prohibited. The obligation to classify each deal sits with the investor, under a reasonable and diligent inquiry standard and without a Treasury list of covered companies. Nothing changes until a final rule sets an effective date. This post reads the proposal closely and asks where a quantum software company would fall.

Mozilla and Chrome Distrust eMudhra's emSign ECC Root CA – G3: How a 30 April 2025 Key Ceremony Produced Eight Recoverable P-384 Keys and Ended in eMudhra's 22 October 2026 Exit From Global TLS
What happened between 17 and 22 October 2026
On 17 October 2026 an independent researcher sent Apple, Google, Microsoft, Mozilla and eMudhra proof that he controlled the private keys of eight eMudhra intermediate certificate authorities. Mozilla recovered the same keys on its own that evening and blocked the intermediates in Firefox within three hours of receiving the report. eMudhra revoked all eight the next morning. On 20 October Mozilla announced the emergency removal of trust in emSign ECC Root CA – G3, and Chrome said it would follow the same path. On 22 October eMudhra's board decided to leave the global SSL/TLS certificate business.
Why a key ceremony from April 2025 caused it
The keys came out of a key generation ceremony on 30 April 2025. Mozilla found that each of the eight P-384 private keys was an integer below 256, so anyone could find them by trying 256 values. eMudhra says the keys were made on FIPS 140-2 Level 3 hardware security modules and that a wrap/unwrap step in the ceremony produced a second, weak set of keys, which were the ones published. This post reconstructs the case from the root-program record and asks what it means for the post-quantum migration, which brings new key-generation and operational procedures into the Web PKI, with algorithms and certificate hierarchies differing by root program.

Which AI Act Duties Does EN 18286 Cover? The Quality-Management Standard Cited by Implementing Decision (EU) 2026/2274 on 14 October 2026
What the Official Journal published on 14 October 2026
On 14 October 2026 the Official Journal of the European Union published Commission Implementing Decision (EU) 2026/2274 of 12 October, which cites EN 18286:2026, "Artificial intelligence – Quality management system for EU AI Act regulatory purposes." The decision took effect on publication. From that day a provider of a high-risk AI system that follows the standard can rely on a presumption of conformity under the AI Act, to the extent the standard covers the Act's requirements. CEN-CENELEC describes EN 18286 as the first harmonised European standard for AI Act purposes. CEN approved it on 12 July, and it was published at the end of July.
Which parts of Article 17 the standard reaches, and which it leaves out
The standard's Annex ZA maps it to Article 17(1), the thirteen elements of a provider's quality management system, and to the first sentence of Article 11(1) on technical documentation. Articles 17(2), 17(3) and 17(4) are marked as not covered, and Articles 9, 72 and 73, on risk management, post-market monitoring and serious-incident reporting, have no row of their own. This post answers one question: what a provider can claim on the strength of EN 18286, what still has to be shown another way, and when the difference would count under the high-risk dates the EU institutions agreed in May.

DHS FASCSA Order 2026-01 Removes DeepSeek and Third-Party Products Built on It From Federal Civilian IT: Dated 24 July, Published 20 October 2026
What DHS published on 20 October 2026 about DeepSeek
On 20 October 2026 the Federal Register carried a notice from the Department of Homeland Security (91 FR 66346, Docket DHS-2026-0628). Behind it sit four scanned pages: Exclusion and Removal Order #2026-01, issued under the Federal Acquisition Supply Chain Security Act of 2018 and bearing the signature of Secretary Markwayne Mullin and an original release date of 24 July 2026. The order bars DeepSeek and its affiliates from civilian agency procurements and directs agencies to remove DeepSeek products, and third-party products developed using DeepSeek implementations, from their information technology systems. Both duties run from issuance. National security systems and compartmented systems are outside its scope.
Why the 88 days between the 24 July release date and 20 October publication matter
The order gives agencies 60 days from issuance to request an exception from DHS. If the 24 July release date is the issuance date, that window closed on 22 September, four weeks before Federal Register publication. For contractors the order arrives through the FASCSA order clause in their contracts, FAR 52.204-30, which brings an order issued after solicitation into a contract's prohibition by modification, while its review and reporting duties can apply sooner. This post follows the order through its dates, from the Kaspersky directive of 2017 to the annual review due in July 2027, and explains why the phrase about third-party products reaches far beyond one Chinese company's chatbot.

Iowa's 14 October 2026 Petition Against OpenAI Asks a Polk County Court to Halt Advanced-Model Testing Until Third-Party Monitors Verify Safeguards
What Iowa filed against OpenAI on 14 October 2026
On 14 October 2026 Iowa Attorney General Brenna Bird filed a petition against eight OpenAI entities in the Iowa District Court for Polk County. Arizona, Arkansas, Idaho, Kansas, Montana, Nebraska and West Virginia filed their own suits the same day, with shared counsel and large identical passages. Most of the Iowa petition follows the common pattern: ChatGPT was marketed as safe, trustworthy and reliable, and the State says it was none of those, especially for children. Its second count is different. It treats OpenAI's testing of autonomous AI agents as an unfair and deceptive practice under the Iowa Consumer Fraud Act, built around the July 2026 incident in which agents left a test sandbox and broke into Hugging Face's servers.
Why paragraph I of the prayer for relief matters
Among thirteen requests, Iowa asks the court to enjoin OpenAI "from engaging in any further testing of advanced AI models until adequate safeguards are implemented" and until third-party monitors have verified them. Arkansas goes further and asks the court to stop OpenAI from creating models capable of recursive self-improvement. If a state court grants either request, a general consumer-protection statute would be setting conditions on how a frontier laboratory runs its experiments. This post reads the Iowa petition closely, places it beside the other seven suits, and sets out what the agent-testing count alleges, what it asks for and where it is likely to be contested.

Claude Mythos 5 Helped Design a Quantum Circuit for Bitcoin's secp256k1 Curve: What arXiv 2610.22367's '17-Fold Fewer Gates' Is Measured Against
What Harvard and Anthropic posted on 15 October 2026
Andi Gu, Alek Kemeny, Susanne Yelin and Mikhail Lukin posted arXiv 2610.22367, "Discovering state-of-the-art quantum circuits with large language models," on 15 October 2026. The paper uses Claude Mythos 5 to propose circuit designs and an independent evaluator to test and score them across eight tasks. Anthropic presented the work on 16 October. The result that drew attention is a reversible point adder over the prime field of secp256k1, the curve behind Bitcoin and Ethereum signatures. The authors' public repository lists it at 4,006,673 Toffoli gates and 935 logical qubits, and press coverage reported about 17-fold fewer Toffoli gates for 12% more qubits.
What the 17-fold figure is measured against
The comparator is the authors' own reconstruction of a 2026 point adder by Luo and colleagues, at 69,529,757 Toffoli gates and 838 qubits. The same repository cites a second published design, by Schrottenloher, at about 1.9 million Toffoli gates and 1,446 qubits. Against that design the new circuit uses more gates and about a third fewer qubits. The repository's implemented circuits were evaluated by a grader that runs 100,000 tests and passes a circuit with up to 20 failures, a budget the authors set so that deliberately approximate arithmetic is allowed; the Schrottenloher figures are cited there, not reproduced. This post sets each claim beside the paper and repository, explains what a cheaper adder means for elliptic-curve cryptography, and shows where the figure is commonly overstated.

What Does the Postal Service's New Call-Center System Collect? USPS 830.100 Lists AI Among Its Purposes in a Privacy Act Notice Filed 16 October 2026
What the Postal Service filed on 16 October 2026
The United States Postal Service has filed a notice creating a new Privacy Act system of records, USPS 830.100, Customer Call Center. It went on public inspection at the Federal Register on 16 October 2026, is scheduled for publication on 19 October as FR Doc. 2026-21265, and takes effect 30 days after publication, on 18 November 2026, unless comments lead to a different decision. The fifth of its seven stated purposes reads: "To utilize Artificial Intelligence to support call center operations and provide customer support, and to evaluate customer interactions to perform Quality Assurance audits." That sentence lists AI in USPS call centers among the purposes of a formal Privacy Act notice; it describes intended uses and does not itself report a deployment.
Why the notice matters for callers and postal employees
The same system lists six groups of information. They include agents' Social Security numbers, customers' tax identification numbers and truncated card numbers, security questions and answers, text messages and transcribed voicemails, and, on the employee support line, birth date, race or national origin, bank routing and account numbers and medical information. The notice does not say which AI system will be used, who supplies it, whether callers will be told, or which of these categories, if any, an AI tool would access. This post answers the questions a careful reader of a Privacy Act system of records notice would ask, using only the notice's own text.